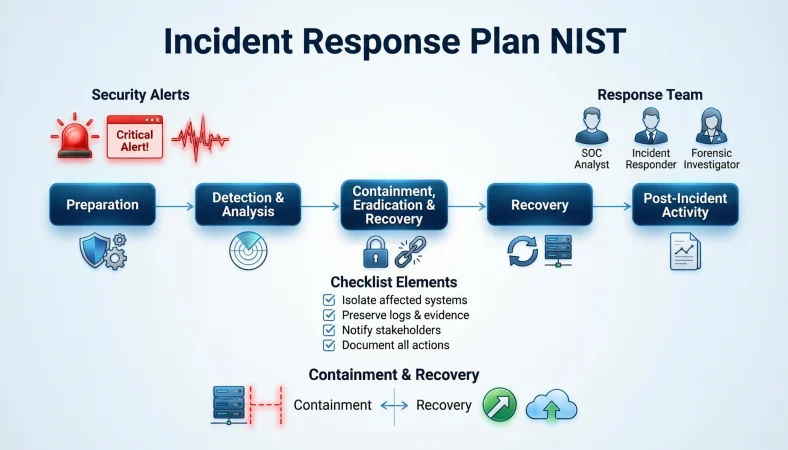
Quick Answer: An incident response plan NIST approach gives organizations a structured way to prepare for, detect, respond to, and recover from cybersecurity incidents. Common alternatives include NIST Incident Response Framework, NIST Cybersecurity Incident Response Plan, NIST Incident Response Guide, NIST Incident Handling Process, NIST SP 800-61.
A security incident rarely arrives at a convenient time. One minute everything looks normal, and the next there is a suspicious login, a ransomware alert, leaked credentials, or a system that suddenly starts acting like it has a mind of its own. That is exactly why an incident response plan NIST approach matters.
Whether you are working in cybersecurity, managing a business, studying information security, or building an internal security process, having a clear response plan can make a huge difference. It helps teams know what to do, who should respond, what evidence to preserve, and how to recover without turning an incident into total chaos.
NIST guidance is commonly used as a practical foundation for organizing incident response activities. The right wording also matters when documenting procedures, writing reports, communicating with employees, or explaining an incident to leadership. Below are ready-to-use responses, statements, and ideas organized by tone and situation.
Funny Incident Response Plan NIST Responses
“Because ‘hope for the best’ is not a security strategy.”
Use this when adding a little humor to a cybersecurity training discussion.
Meaning: A proper plan is more reliable than simply hoping nothing goes wrong.
“The incident has entered the chat.”
Use this when introducing an unexpected security event during a presentation.
Meaning: It humorously signals that an incident has officially appeared.
“First rule of incident response: do not panic-click.”
Use this when teaching employees how to react to suspicious alerts.
Meaning: The response should be controlled instead of impulsive.
“Cybersecurity emergencies do not wait for coffee.”
Use this when discussing the need for preparedness.
Meaning: Teams need procedures that work even when incidents happen unexpectedly.
“The firewall had one job, but apparently we need a backup plan.”
Use this during a lighthearted security awareness session.
Meaning: Multiple defensive layers and response procedures are important.
“Today’s forecast: 100% chance of incident response.”
Use this for a playful cybersecurity presentation slide.
Meaning: Security teams must be ready for unexpected incidents.
“Keep calm and follow the playbook.”
Use this when reminding staff to follow established procedures.
Meaning: A documented process helps people stay focused during an incident.
“Plot twist: the suspicious login was actually suspicious.”
Use this when discussing detection and investigation.
Meaning: Alerts should be investigated rather than casually dismissed.
“No plan? Congratulations, you just unlocked hard mode.”
Use this when explaining the risks of poor preparation.
Meaning: Responding without preparation usually creates unnecessary difficulty.
“Incident response: because screenshots are not a strategy.”
Use this when explaining the need for formal documentation.
Meaning: Security incidents require structured actions and records.
“When in doubt, follow the documented process.”
Use this for security awareness messaging.
Meaning: Established procedures provide direction during uncertainty.
“Cybersecurity loves a good checklist.”
Use this when introducing incident response documentation.
Meaning: Checklists can help teams avoid missing important steps.
Professional Incident Response Plan NIST Responses
“The incident response process should begin with established roles and responsibilities.”
Use this in professional security documentation.
Meaning: Everyone should understand their role before an incident occurs.
“The organization should follow a documented incident response procedure.”
Use this in policies and internal reports.
Meaning: Response actions should be guided by an approved process.
“All suspected incidents should be assessed according to established criteria.”
Use this in an incident handling procedure.
Meaning: Teams need consistent standards for evaluating events.
“Relevant evidence should be preserved throughout the investigation.”
Use this in forensic response documentation.
Meaning: Important information should be protected from alteration or loss.
“Incident communications should follow the organization’s escalation process.”
Use this in response plans and policies.
Meaning: Security communications should reach the appropriate people promptly.
“Response activities should be documented throughout the incident lifecycle.”
Use this in security operations procedures.
Meaning: Teams should maintain a record of important actions and decisions.
“Containment measures should be selected based on the nature and impact of the incident.”
Use this when documenting response decisions.
Meaning: Containment should match the specific circumstances.
“Recovery activities should be coordinated with relevant technical and business teams.”
Use this in business continuity documentation.
Meaning: Restoring systems requires cooperation across departments.
“Lessons learned should be incorporated into future response improvements.”
Use this after an incident review.
Meaning: Each incident can help strengthen future preparedness.
“Incident severity should guide escalation and response priorities.”
Use this in an incident classification procedure.
Meaning: More serious incidents require appropriately prioritized action.
“Incident records should provide a clear timeline of significant events.”
Use this when preparing investigation documentation.
Meaning: A timeline helps explain what happened and when.
“The response plan should be reviewed and updated regularly.”
Use this in security governance documents.
Meaning: Response procedures should remain relevant as threats and systems change.
Practical Incident Response Plan NIST Responses
“Identify the incident, assess its scope, and determine the appropriate response.”
Use this as a concise procedural statement.
Meaning: The initial response should establish what happened and how serious it is.
“Start by confirming whether the alert represents a genuine security incident.”
Use this during initial triage.
Meaning: Analysts should distinguish real incidents from false positives.
“Document what is known before making major response decisions.”
Use this during early investigation.
Meaning: Accurate information helps teams make better decisions.
“Preserve relevant logs before they are overwritten.”
Use this during evidence collection.
Meaning: Important investigation data can disappear if it is not retained promptly.
“Separate affected systems when containment is necessary.”
Use this when documenting containment actions.
Meaning: Isolation can help limit further damage.
“Escalate incidents according to their severity and business impact.”
Use this in an escalation procedure.
Meaning: Serious incidents should reach the appropriate decision-makers.
“Record every significant action taken during the response.”
Use this in incident documentation.
Meaning: Detailed records support accountability and later analysis.
“Coordinate technical response with business priorities.”
Use this during recovery planning.
Meaning: Security actions should consider operational needs.
“Confirm system integrity before returning affected services to normal operation.”
Use this during recovery.
Meaning: Systems should be checked before being fully restored.
“Review the incident after recovery to identify improvement opportunities.”
Use this during post-incident activities.
Meaning: A review helps prevent similar problems.
“Update procedures when lessons from an incident reveal a gap.”
Use this after a security event.
Meaning: Lessons learned should lead to practical improvements.
“Keep the response process clear enough to follow under pressure.”
Use this when designing an incident response plan.
Meaning: A useful plan should work during stressful situations.
Clear And Simple Incident Response Plan NIST Responses
“Know what happened before deciding what to do next.”
Use this when explaining incident triage to beginners.
Meaning: Understanding the situation should guide the response.
“Protect the evidence and document your actions.”
Use this as a simple security reminder.
Meaning: Evidence preservation and documentation are essential.
“Contain the problem before it spreads.”
Use this when explaining containment.
Meaning: Response teams should work to limit additional impact.
“Tell the right people at the right time.”
Use this when explaining escalation.
Meaning: Communication should reach appropriate stakeholders promptly.
“Follow the plan instead of improvising everything.”
Use this during employee security training.
Meaning: Established procedures reduce confusion.
“Know who owns each response task.”
Use this when designing team responsibilities.
Meaning: Clear ownership prevents important tasks from being overlooked.
“Keep a timeline of what happened.”
Use this when teaching incident documentation.
Meaning: A timeline makes the investigation easier to understand.
“Do not delete useful evidence.”
Use this when discussing incident handling basics.
Meaning: Investigation data may be critical for understanding the event.
“Recover carefully, not just quickly.”
Use this when discussing system restoration.
Meaning: Fast recovery should not compromise security.
“Review the incident when the immediate danger is over.”
Use this after an incident.
Meaning: Post-incident analysis can reveal weaknesses.
“Turn lessons learned into action.”
Use this in improvement planning.
Meaning: Reviews should produce practical security changes.
“Make the plan easy to find before you need it.”
Use this when creating response documentation.
Meaning: A plan is only useful if responders can access it when needed.
Confident Incident Response Plan NIST Responses
“We have a defined process for handling security incidents.”
Use this when explaining organizational preparedness.
Meaning: The organization has established procedures for responding to incidents.
“Every incident is assessed based on evidence and impact.”
Use this in professional communications.
Meaning: Response decisions are based on information rather than assumptions.
“Our response process includes clear escalation paths.”
Use this when describing incident governance.
Meaning: Serious situations can be directed to appropriate leaders.
“We document response actions throughout the investigation.”
Use this in an audit or security review.
Meaning: Important response activities are recorded.
“Containment decisions are based on the circumstances of the incident.”
Use this when explaining technical response decisions.
Meaning: Teams select containment actions appropriate to the event.
“Recovery follows defined security and operational checks.”
Use this when discussing system restoration.
Meaning: Services are restored through controlled procedures.
“Our incident response plan is designed for real-world events.”
Use this in a security program overview.
Meaning: The plan is intended to support practical incident handling.
“We review incidents to strengthen future response capabilities.”
Use this after a security event.
Meaning: Incidents are used as opportunities for improvement.
“Roles are established before an incident occurs.”
Use this when explaining preparedness.
Meaning: Responders know their responsibilities ahead of time.
“Communication is part of the response, not an afterthought.”
Use this in incident management discussions.
Meaning: Timely communication is an important response activity.
“Preparedness gives responders a clearer path forward.”
Use this in a cybersecurity presentation.
Meaning: Planning can reduce uncertainty during incidents.
“A documented process helps turn uncertainty into coordinated action.”
Use this when describing the value of an incident response plan.
Meaning: Documentation helps teams respond in an organized way.
Clever Incident Response Plan NIST Responses
“The best time to build an incident response plan is before the incident.”
Use this as a cybersecurity presentation opener.
Meaning: Preparation should happen before an emergency.
“Detection starts the conversation, but response completes the job.”
Use this when explaining the broader response process.
Meaning: Finding an incident is only one part of handling it.
“A security alert is information, not automatically a conclusion.”
Use this during analyst training.
Meaning: Alerts require investigation before final decisions.
“Containment without context can create new problems.”
Use this when discussing response decisions.
Meaning: Containment actions should consider technical and business consequences.
“Good documentation tells the story after the adrenaline fades.”
Use this during incident response training.
Meaning: Records help reconstruct events after the immediate crisis.
“An incident timeline turns scattered evidence into a clearer picture.”
Use this during investigation planning.
Meaning: Chronological records help analysts understand events.
“The response plan is the map; the incident is the terrain.”
Use this in a cybersecurity presentation.
Meaning: A plan provides direction while real incidents may require adaptation.
“Preparation turns reaction into coordinated response.”
Use this when discussing cybersecurity maturity.
Meaning: Planning helps teams act systematically.
“Recovery is not finished until security is considered.”
Use this during restoration planning.
Meaning: Restoring operations should include security checks.
“Every incident can become tomorrow’s security lesson.”
Use this after an incident review.
Meaning: Organizations can learn from security events.
“A checklist cannot replace judgment, but it can protect against forgotten steps.”
Use this when discussing response playbooks.
Meaning: Checklists support responders without eliminating professional judgment.
“The quietest incident response plan is the one nobody needs to improvise.”
Use this in security awareness content.
Meaning: Good preparation reduces unnecessary confusion.
Technical Incident Response Plan NIST Responses
“Begin with incident identification and initial analysis.”
Use this in technical documentation.
Meaning: Responders first determine whether suspicious activity represents an incident.
“Collect relevant logs and system information.”
Use this during technical investigation.
Meaning: Logs and system data can provide evidence about what occurred.
“Preserve evidence according to established forensic procedures.”
Use this when documenting investigation activities.
Meaning: Evidence should be handled carefully to maintain its usefulness.
“Apply containment controls appropriate to the affected environment.”
Use this in a technical response plan.
Meaning: Technical isolation should reflect the specific environment.
“Determine affected assets, accounts, systems, and services.”
Use this during scope assessment.
Meaning: Understanding the affected resources helps determine the incident’s reach.
“Analyze indicators associated with the suspected incident.”
Use this during investigation.
Meaning: Relevant indicators can help establish what happened.
“Coordinate remediation with system owners and security teams.”
Use this during recovery planning.
Meaning: Technical fixes often require cooperation across teams.
“Validate systems before returning them to production.”
Use this during recovery.
Meaning: Restored systems should be checked before normal operation resumes.
“Monitor affected systems after recovery.”
Use this when documenting post-recovery activities.
Meaning: Continued monitoring can help identify recurring suspicious activity.
“Record timestamps, actions, findings, and decisions.”
Use this during incident documentation.
Meaning: Detailed records support investigation and review.
“Use incident severity to prioritize technical response activities.”
Use this in a technical playbook.
Meaning: Response resources should be focused according to risk and impact.
“Feed investigation findings into future detection and response improvements.”
Use this during post-incident analysis.
Meaning: Lessons from investigations can improve security capabilities.
Calm Incident Response Plan NIST Responses
“Pause, assess, and follow the established response process.”
Use this when teams face an unexpected security alert.
Meaning: A calm and structured response reduces confusion.
“We will work through the incident step by step.”
Use this when reassuring a response team.
Meaning: The situation can be managed through organized actions.
“Let’s confirm the facts before making assumptions.”
Use this during an uncertain investigation.
Meaning: Decisions should be based on verified information.
“We have procedures in place for situations like this.”
Use this when communicating with stakeholders.
Meaning: The organization has prepared for incident response.
“Let’s focus first on understanding the scope.”
Use this during initial triage.
Meaning: Establishing the incident’s reach is an important early activity.
“We can escalate when the evidence and impact require it.”
Use this during response coordination.
Meaning: Escalation should follow established criteria.
“Document what we know and keep moving methodically.”
Use this during an active incident.
Meaning: Accurate documentation and steady action help maintain control.
“Containment comes with careful consideration.”
Use this when discussing response options.
Meaning: Isolation decisions should account for the circumstances.
“We will verify before restoring affected services.”
Use this during recovery.
Meaning: Recovery should include appropriate validation.
“The immediate response comes first, then the lessons learned.”
Use this after stabilizing an incident.
Meaning: Teams should handle urgent needs before conducting the broader review.
“One step at a time is still a response strategy.”
Use this to keep teams focused.
Meaning: Structured progress can be more effective than rushed action.
“Clear procedures make stressful situations easier to manage.”
Use this in cybersecurity training.
Meaning: Preparedness can reduce uncertainty during incidents.
Strategic Incident Response Plan NIST Responses
“Incident response should support both security and business objectives.”
Use this in security strategy discussions.
Meaning: Response planning should consider operational priorities as well as technical concerns.
“Incident severity should influence resource allocation.”
Use this during response planning.
Meaning: More significant incidents may require additional attention and resources.
“Response planning should account for critical business services.”
Use this when developing organizational procedures.
Meaning: Security incidents can affect important business operations.
“Roles should be defined across technical, legal, communications, and management functions.”
Use this in enterprise response planning.
Meaning: Major incidents can require multiple organizational disciplines.
“Escalation criteria should be established before an incident occurs.”
Use this in governance documentation.
Meaning: Teams should not have to invent escalation rules during a crisis.
“Response plans should align with broader business continuity efforts.”
Use this during resilience planning.
Meaning: Cybersecurity response and operational continuity should work together.
“Incident metrics can help identify recurring response weaknesses.”
Use this during security program reviews.
Meaning: Measurements can reveal areas needing improvement.
“Tabletop exercises can help validate response procedures.”
Use this during preparedness planning.
Meaning: Practice can reveal gaps before a real incident occurs.
“Response plans should reflect the organization’s technology environment.”
Use this when reviewing documentation.
Meaning: Generic procedures may need adaptation to actual systems.
“Third-party dependencies should be considered during incident planning.”
Use this in enterprise security planning.
Meaning: Vendors and service providers may affect response and recovery.
“Communication plans should identify key stakeholders and escalation channels.”
Use this when building response procedures.
Meaning: Teams need defined ways to communicate during incidents.
“Post-incident findings should influence future security investments.”
Use this after an incident review.
Meaning: Lessons learned can inform future improvements.
Sarcastic Incident Response Plan NIST Responses
“Because apparently ‘turn it off and hope’ needed an upgrade.”
Use this when joking about informal security practices.
Meaning: Structured incident response is preferable to improvised fixes.
“Nothing says preparedness like searching for the incident plan during the incident.”
Use this during security awareness training.
Meaning: Response documentation should be prepared and accessible beforehand.
“Sure, let’s make every incident a surprise meeting.”
Use this when discussing the problems caused by unclear procedures.
Meaning: Defined roles can prevent unnecessary confusion.
“The password was ‘password,’ but at least we have a response plan.”
Use this in a light cybersecurity presentation.
Meaning: Security planning cannot replace good preventive practices.
“Who needs documentation when everyone remembers everything perfectly?”
Use this when emphasizing the importance of records.
Meaning: Written documentation is more reliable than memory.
“Because guessing the next step is definitely efficient.”
Use this when explaining why playbooks matter.
Meaning: Prepared procedures reduce unnecessary uncertainty.
“The incident is urgent, but the plan should have been ready yesterday.”
Use this during preparedness discussions.
Meaning: Response planning needs to happen before an incident.
“Nothing builds teamwork like an unexplained security alert.”
Use this in a cybersecurity training presentation.
Meaning: Clear responsibilities are especially valuable during unexpected events.
“Let’s just restore everything and ask questions later.”
Use this as an example of poor recovery practice.
Meaning: Recovery should be controlled and security-conscious.
“Documentation? Surely future us will remember every detail.”
Use this when teaching incident reporting.
Meaning: Teams should document events while information is fresh.
“The alert says critical, so naturally everyone should panic.”
Use this when explaining alert triage.
Meaning: Severity indicators should guide assessment, not trigger uncontrolled reactions.
“If improvisation were a security framework, we would all be experts.”
Use this when discussing formal response procedures.
Meaning: Structured frameworks provide more reliable guidance than improvisation.
Creative Incident Response Plan NIST Responses
“Build your response plan like a fire escape: useful before the emergency and essential during it.”
Use this in a security awareness article.
Meaning: Preparedness matters before an incident occurs.
“Think of incident response as a team sport, not a solo mission.”
Use this when explaining cross-functional response.
Meaning: Effective response often requires multiple roles working together.
“Give every incident a timeline, a team, and a next step.”
Use this as a planning principle.
Meaning: Clear ownership, chronology, and action improve coordination.
“Turn every post-incident lesson into a future defense.”
Use this during security improvement planning.
Meaning: Lessons learned should strengthen future security.
“Make the playbook simple enough to use when everyone’s stress level is at 100%.”
Use this when designing procedures.
Meaning: Response documentation should remain usable under pressure.
“A good response plan answers the ‘who, what, when, and now what?’ questions.”
Use this during training.
Meaning: Effective planning addresses responsibilities, actions, timing, and next steps.
“Treat every incident as a story that needs a clear beginning, middle, and recovery.”
Use this during incident documentation training.
Meaning: A structured timeline helps explain the full event.
“Put the right people around the right problem.”
Use this when discussing incident roles.
Meaning: Response responsibilities should match expertise.
“Create procedures that work in real life, not just on paper.”
Use this during plan development.
Meaning: Plans should be practical and testable.
“Practice the plan before the threat gets a speaking role.”
Use this when recommending exercises.
Meaning: Organizations should test procedures before real incidents.
“Make your incident response plan a living document.”
Use this during security governance discussions.
Meaning: Procedures should evolve as technology and lessons change.
“Turn yesterday’s incident into tomorrow’s checklist.”
Use this during post-incident reviews.
Meaning: Past experiences can inform future response procedures.
Emotional Incident Response Plan NIST Responses
“A security incident can feel overwhelming, but a clear plan gives the team direction.”
Use this when supporting employees during an incident.
Meaning: Structured procedures can reduce uncertainty.
“Preparedness helps people focus on action instead of fear.”
Use this during security awareness training.
Meaning: Planning can make stressful situations more manageable.
“Every documented step can remove one more unknown.”
Use this when explaining the value of procedures.
Meaning: Documentation provides clarity during uncertainty.
“Good incident response protects more than systems; it protects trust.”
Use this in organizational security communications.
Meaning: Effective response can also support confidence among stakeholders.
“The goal is not perfection; it is a coordinated response.”
Use this when discussing incident management.
Meaning: Teams should focus on organized action rather than expecting flawless execution.
“Mistakes should become lessons, not permanent weaknesses.”
Use this during post-incident reviews.
Meaning: Organizations should learn from response problems.
“A difficult incident can reveal exactly where the plan needs work.”
Use this after an incident.
Meaning: Problems exposed during an event can guide improvements.
“Security teams need clarity as much as they need technology.”
Use this in a cybersecurity presentation.
Meaning: Clear processes are an important part of effective response.
“Recovery is also about rebuilding confidence.”
Use this when discussing post-incident communication.
Meaning: Recovery can involve restoring trust alongside systems.
“A strong response starts with people knowing what they are responsible for.”
Use this in team training.
Meaning: Clear responsibilities support coordinated action.
“Every lesson documented today can make tomorrow’s response smoother.”
Use this during post-incident reviews.
Meaning: Documentation can improve future preparedness.
“Security is easier to manage when everyone knows the next step.”
Use this when discussing response procedures.
Meaning: Clear direction helps teams act consistently.
Friendly Incident Response Plan NIST Responses
“Let’s keep the process simple, clear, and easy to follow.”
Use this when designing a team response procedure.
Meaning: Practical plans are easier to use during stressful situations.
“We have a plan, and we can work through it together.”
Use this when reassuring a response team.
Meaning: Collaboration can make incident handling more manageable.
“Let’s gather the facts first and then decide on the next step.”
Use this during initial investigation.
Meaning: Decisions should follow factual assessment.
“Everyone has a role, so let’s keep communication clear.”
Use this during incident coordination.
Meaning: Clear communication supports teamwork.
“We will document what happens as we go.”
Use this when starting an incident investigation.
Meaning: Ongoing documentation keeps the response record accurate.
“Let’s make sure the right people are informed.”
Use this during escalation.
Meaning: Stakeholders should receive appropriate information.
“We can review what worked and what did not afterward.”
Use this after an incident.
Meaning: Post-incident review can identify improvements.
“The goal is to restore services safely.”
Use this during recovery discussions.
Meaning: Recovery should balance operational needs with security.
“Let’s keep everyone focused on the facts.”
Use this during an uncertain incident.
Meaning: Fact-based communication helps prevent unnecessary confusion.
“We can update the plan when we learn something new.”
Use this during response planning.
Meaning: Procedures should evolve when new information becomes available.
“A clear checklist can make a stressful situation easier.”
Use this during security training.
Meaning: Checklists can help responders remember important tasks.
“Prepared teams handle unexpected moments with more confidence.”
Use this in awareness content.
Meaning: Preparation supports calm and coordinated action.
Educational Incident Response Plan NIST Responses
“NIST provides structured guidance that organizations can use to improve incident response.”
Use this in an educational article.
Meaning: NIST guidance can serve as a foundation for response planning.
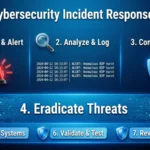
“Incident response is the organized process of addressing cybersecurity incidents.”
Use this when introducing the topic to beginners.
Meaning: Incident response coordinates actions before, during, and after security events.
“Preparation helps organizations establish capabilities before incidents occur.”
Use this in cybersecurity coursework.
Meaning: Readiness is an important part of effective response.
“Detection helps organizations recognize potentially harmful activity.”
Use this when explaining the incident lifecycle.
Meaning: Teams need ways to identify suspicious events.
“Analysis helps determine what an incident involves.”
Use this in training material.
Meaning: Investigation helps establish scope, cause, and impact.
“Containment focuses on limiting additional impact.”
Use this when teaching response concepts.
Meaning: Containment aims to control the spread or consequences of an incident.
“Eradication focuses on addressing the source or components of the incident.”
Use this in cybersecurity coursework.
Meaning: The organization works to remove the underlying threat.
“Recovery focuses on restoring affected systems and services.”
Use this in an incident response lesson.
Meaning: Recovery returns operations to an appropriate state.
“Post-incident activity helps organizations identify lessons and improvements.”
Use this after explaining recovery.
Meaning: Incident response continues through learning and improvement.
“Incident response plans should define responsibilities before emergencies happen.”
Use this in a classroom presentation.
Meaning: Predefined roles reduce confusion during an incident.
“Documentation supports communication, investigation, and later review.”
Use this in an educational explanation.
Meaning: Accurate records serve several important response purposes.
“Testing response procedures can reveal weaknesses before a real incident occurs.”
Use this when discussing preparedness exercises.
Meaning: Practice can expose gaps in plans and procedures.
FAQs
What Does Incident Response Plan NIST Mean?
An incident response plan NIST approach refers to using NIST guidance and structured cybersecurity practices to prepare for, detect, respond to, and recover from security incidents.
What Is The Emotional Or Flirty Interpretation?
This keyword is technical rather than emotional or flirty. It is generally used in cybersecurity, information technology, compliance, risk management, and business security discussions.
What Is The Professional Or Formal Usage?
Professionally, it can describe an organization’s documented process for managing cybersecurity incidents, including responsibilities, escalation, investigation, containment, recovery, communication, and lessons learned.
What Should You Say If You Do Not Actually Mean It?
If you are discussing an incident response plan professionally, avoid vague wording. State what has actually been documented, tested, approved, or implemented instead of implying that a complete plan exists when it does not.
Is Humor Appropriate When Discussing Incident Response Plans?
Light humor can work in training sessions, presentations, or social content, but serious incidents require clear, professional communication. Match the tone to the audience, severity, and situation.
Conclusion
A good incident response plan is more than a document sitting quietly in a shared folder. It gives people direction when a security incident creates confusion, pressure, and plenty of questions. Whether you need a professional statement, a training-friendly explanation, a clever line, or a practical response, the right wording can make cybersecurity concepts much easier to communicate.
The NIST approach can also help organizations think more systematically about preparation, detection, response, recovery, documentation, and improvement. Try different responses from this list depending on your audience and situation. Save this guide, share it with your security team, and reuse the lines that fit your next presentation, policy, or training session. Keep it clear, keep it practical, and keep improving your response plan.