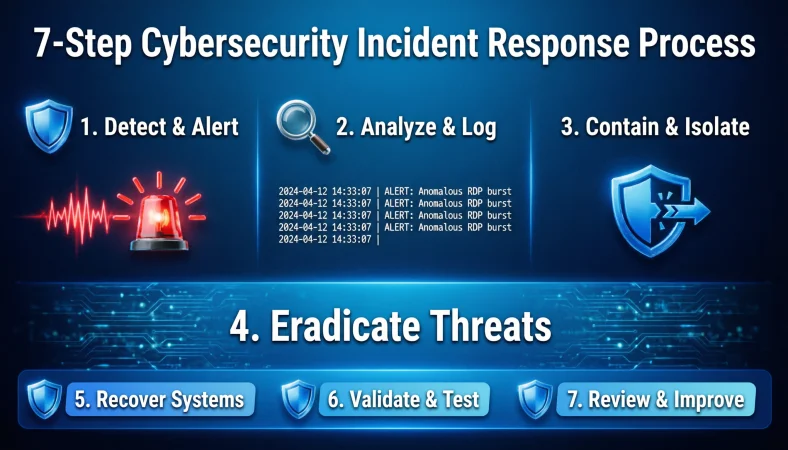
Quick Answer: Security incident response steps usually include preparation, detection, analysis, containment, eradication, recovery, and lessons learned. The right approach helps teams respond quickly, reduce damage, and restore normal operations.
Top alternatives: Prepare and detect, analyze the incident, contain the threat, eradicate the cause, recover and review
Security incidents rarely arrive with a polite calendar invite. One minute everything is normal, and the next there is a suspicious login, strange network traffic, a phishing email, or an alert that makes everyone sit up a little straighter. Whether you are handling cybersecurity at work, studying incident response, or simply trying to understand what happens after an alert, knowing the right security incident response steps can make the situation far less overwhelming. The goal is not to panic or start clicking random buttons.
It is to follow a structured process that helps identify what happened, limit the damage, remove the threat, and safely return to normal operations. Good incident response is about speed, communication, teamwork, and smart decisions. In this guide, you will find practical, easy-to-understand ways to describe and approach each stage, plus useful wording for teams, reports, messages, and real-world situations.
Funny Security Incident Response Steps
1. Check the alert before blaming the Wi-Fi.
Use this when a suspicious alert appears and everyone immediately suspects the network.
Meaning: It encourages verification before jumping to conclusions.
2. Stay calm, the firewall has seen worse.
Use this when the team needs a little humor during a stressful incident.
Meaning: It reminds everyone to remain composed.
3. First we investigate, then we panic responsibly.
Use this when joking about the pressure of an active incident.
Meaning: It puts investigation ahead of emotional reactions.
4. Find the problem before it finds another laptop.
Use this when emphasizing the importance of quick investigation.
Meaning: It highlights the need to identify threats early.
5. Nobody touch anything suspicious. Seriously.
Use this when users are tempted to interact with questionable files or links.
Meaning: It promotes caution during an investigation.
6. The alert is not going to investigate itself.
Use this when motivating a team to begin analysis.
Meaning: It encourages immediate action.
7. Let’s contain the chaos before it gets a sequel.
Use this when discussing containment during a growing incident.
Meaning: It stresses stopping further spread.
8. Screenshot first, detective work second.
Use this when preserving useful evidence before making changes.
Meaning: It encourages documentation before intervention.
9. One suspicious login and suddenly everyone is Sherlock.
Use this when multiple people start investigating the same alert.
Meaning: It humorously describes a sudden investigative rush.
10. Rebooting is not an incident response strategy.
Use this when someone suggests restarting a compromised system as the first solution.
Meaning: It encourages proper investigation instead of shortcuts.
11. The logs know things we do not.
Use this when reminding people to review system records.
Meaning: It emphasizes the value of evidence.
12. Secure first, celebrate later.
Use this when the team is tempted to declare victory too early.
Meaning: It reinforces finishing the response before relaxing.
Practical Security Incident Response Steps
1. Start with preparation.
Use this when explaining the first stage of an organized response program.
Meaning: It highlights readiness before an incident occurs.
2. Detect the warning signs early.
Use this when discussing alerts, anomalies, and suspicious activity.
Meaning: It emphasizes early identification.
3. Confirm whether an incident occurred.
Use this when an alert needs validation before escalation.
Meaning: It separates genuine incidents from false alarms.
4. Analyze what happened.
Use this when beginning technical investigation.
Meaning: It focuses attention on understanding the event.
5. Identify affected systems.
Use this when determining the scope of an incident.
Meaning: It helps establish which assets may be involved.
6. Contain the threat quickly.
Use this when explaining how teams prevent additional damage.
Meaning: It focuses on limiting the incident.
7. Preserve relevant evidence.
Use this when forensic information may be needed later.
Meaning: It protects information needed for investigation.
8. Remove the root cause.
Use this when discussing eradication after containment.
Meaning: It focuses on eliminating the source of the problem.
9. Restore systems safely.
Use this when explaining the recovery stage.
Meaning: It emphasizes careful restoration.
10. Monitor after recovery.
Use this when systems have returned to normal operation.
Meaning: It encourages continued observation for recurring threats.
11. Document every major decision.
Use this when maintaining an incident timeline.
Meaning: It creates an accurate record for review.
12. Learn from the incident.
Use this after operations have stabilized.
Meaning: It turns an incident into an opportunity to improve defenses.
Professional Security Incident Response Steps
1. Initiate the incident response procedure.
Use this in formal workplace communication after an incident is confirmed.
Meaning: It signals the beginning of an organized response.
2. Assess the incident severity.
Use this when determining how urgently the situation requires attention.
Meaning: It supports appropriate prioritization.
3. Establish the incident scope.
Use this when documenting potentially affected assets.
Meaning: It defines the boundaries of the incident.
4. Assign response responsibilities.
Use this when coordinating security, IT, legal, or management teams.
Meaning: It clarifies who handles each responsibility.
5. Maintain a documented timeline.
Use this when recording important actions and discoveries.
Meaning: It creates a reliable incident history.
6. Apply appropriate containment measures.
Use this when formally describing threat isolation.
Meaning: It focuses on reducing further exposure.
7. Preserve forensic evidence.
Use this when evidence may support technical or legal investigation.
Meaning: It protects information needed for analysis.
8. Complete the eradication process.
Use this when the identified threat has been removed.
Meaning: It confirms that remediation has progressed.
9. Validate system integrity before restoration.
Use this before returning affected systems to normal use.
Meaning: It promotes safer recovery.
10. Communicate verified findings.
Use this when providing updates to stakeholders.
Meaning: It encourages accurate, evidence-based reporting.
11. Conduct a post-incident review.
Use this after recovery has been completed.
Meaning: It supports organizational learning.
12. Update controls based on findings.
Use this when improving defenses after an incident.
Meaning: It turns lessons into practical improvements.
Cybersecurity Security Incident Response Steps
1. Review the initial security alert.
Use this when a monitoring system reports suspicious activity.
Meaning: It begins technical validation.
2. Correlate relevant security events.
Use this when multiple alerts may belong to one incident.
Meaning: It helps connect related evidence.
3. Identify indicators of compromise.
Use this when searching for technical signs of malicious activity.
Meaning: It helps establish whether compromise occurred.
4. Determine the attack vector.
Use this when investigating how the incident may have started.
Meaning: It focuses on the likely entry point.
5. Identify compromised accounts or assets.
Use this when investigating possible unauthorized access.
Meaning: It defines potentially affected resources.
6. Isolate affected systems when appropriate.
Use this when discussing containment of potentially compromised devices.
Meaning: It limits possible spread.
7. Review authentication activity.
Use this when suspicious account behavior is involved.
Meaning: It can reveal unusual access patterns.
8. Examine relevant logs.
Use this when investigators need supporting evidence.
Meaning: It helps reconstruct activity.
9. Remove confirmed malicious artifacts.
Use this during remediation after evidence has been preserved.
Meaning: It addresses identified threats.
10. Reset affected credentials when necessary.
Use this when account compromise is suspected.
Meaning: It helps reduce unauthorized access risk.
11. Verify defensive controls.
Use this after remediation activities are completed.
Meaning: It checks whether protections are functioning properly.
12. Document technical findings.
Use this when preparing an incident report.
Meaning: It creates a clear record of what was discovered.
Incident Detection And Analysis Steps
1. Validate the alert.
Use this when deciding whether a notification represents a real security issue.
Meaning: It prevents unnecessary escalation.
2. Determine what changed.
Use this when comparing normal and suspicious activity.
Meaning: It helps identify strange behavior.
3. Establish the first known event.
Use this when building an incident timeline.
Meaning: It helps identify when the activity began.
4. Identify affected users.
Use this when suspicious activity involves accounts or identities.
Meaning: It helps determine potential exposure.
5. Identify affected devices.
Use this when endpoint activity appears unusual.
Meaning: It helps define the technical scope.
6. Review surrounding events.
Use this when a single alert does not tell the full story.
Meaning: It provides additional context.
7. Compare activity against known baselines.
Use this when normal behavior needs to be distinguished from anomalies.
Meaning: It supports more accurate analysis.
8. Classify the incident.
Use this when deciding what type of security event occurred.
Meaning: It helps guide response decisions.
9. Assess potential impact.
Use this when determining business or technical consequences.
Meaning: It helps prioritize response efforts.
10. Confirm the scope before containment.
Use this when investigators need enough information to act intelligently.
Meaning: It reduces unnecessary disruption.
11. Record evidence and observations.
Use this throughout the investigation.
Meaning: It preserves important details.
12. Escalate when the risk warrants it.
Use this when an incident exceeds normal handling procedures.
Meaning: It ensures serious incidents receive proper attention.
Containment Security Incident Response Steps
1. Isolate the affected system.
Use this when a device may be actively compromised.
Meaning: It limits possible communication or spread.
2. Restrict suspicious access.
Use this when unauthorized activity is suspected.
Meaning: It reduces opportunities for continued access.
3. Protect critical systems first.
Use this when resources must be prioritized during containment.
Meaning: It focuses protection on high-value assets.
4. Segment affected network areas.
Use this when network exposure needs to be reduced.
Meaning: It can limit movement between systems.
5. Disable compromised accounts when appropriate.
Use this when account misuse is confirmed or strongly suspected.
Meaning: It prevents further unauthorized activity.
6. Block confirmed malicious indicators.
Use this when defensive controls can safely restrict known threats.
Meaning: It reduces continued exposure.
7. Preserve evidence before major changes.
Use this when investigation requirements must be considered.
Meaning: It prevents useful evidence from being lost.
8. Monitor containment actions.
Use this when changes could affect other systems.
Meaning: It confirms that containment is working.
9. Reassess the incident after isolation.
Use this when new evidence appears during containment.
Meaning: It keeps the response aligned with current facts.
10. Coordinate containment with stakeholders.
Use this when business teams may be affected by technical actions.
Meaning: It balances security and operational needs.
11. Avoid unnecessary disruption.
Use this when containment options could affect important services.
Meaning: It encourages proportionate action.
12. Confirm that the threat is contained.
Use this before moving fully into eradication.
Meaning: It establishes that further spread is controlled.
Eradication And Recovery Steps
1. Remove the confirmed threat.
Use this when the incident has been contained and remediation begins.
Meaning: It focuses on eliminating the identified cause.
2. Address the vulnerability involved.
Use this when a weakness contributed to the incident.
Meaning: It reduces the chance of recurrence.
3. Clean affected systems carefully.
Use this when malicious artifacts have been identified.
Meaning: It supports a safer recovery.
4. Restore from trusted sources.
Use this when systems or data need restoration.
Meaning: It reduces the risk of restoring compromised content.
5. Validate system security before reconnecting.
Use this before returning systems to normal operations.
Meaning: It confirms that recovery is reasonably safe.
6. Re-enable services gradually.
Use this when systems are being returned to production.
Meaning: It allows closer monitoring during recovery.
7. Monitor restored systems.
Use this after services return online.
Meaning: It helps detect signs of recurring compromise.
8. Verify user access.
Use this when account changes were made during response.
Meaning: It confirms that legitimate access works correctly.
9. Confirm business operations are stable.
Use this when recovery affects important services.
Meaning: It checks whether normal operations have resumed.
10. Keep recovery evidence documented.
Use this when recording restoration actions.
Meaning: It provides a traceable recovery record.
11. Watch for repeated indicators.
Use this after remediation is complete.
Meaning: It helps identify possible persistence.
12. Close the incident only after validation.
Use this when deciding whether response activities are complete.
Meaning: It prevents premature closure.
Security Incident Response Steps For Teams
1. Create one clear incident owner.
Use this when several people are involved in response.
Meaning: It prevents confusion over responsibility.
2. Keep communication focused.
Use this during a fast-moving incident.
Meaning: It reduces unnecessary noise.
3. Share verified information first.
Use this when communicating incident updates.
Meaning: It reduces speculation.
4. Give each person a defined role.
Use this when organizing a response team.
Meaning: It improves coordination.
5. Keep technical and business teams aligned.
Use this when security actions affect operations.
Meaning: It encourages cross-team cooperation.
6. Record important decisions.
Use this throughout the response process.
Meaning: It creates accountability.
7. Escalate serious findings quickly.
Use this when the incident becomes more significant.
Meaning: It ensures appropriate leadership involvement.
8. Avoid assigning blame during response.
Use this when emotions begin running high.
Meaning: It keeps attention on solving the problem.
9. Ask for evidence, not guesses.
Use this when different explanations are being discussed.
Meaning: It promotes fact-based investigation.
10. Keep stakeholders updated appropriately.
Use this when business leaders need incident information.
Meaning: It supports informed decision-making.
11. Review the response as a team.
Use this after the incident is resolved.
Meaning: It encourages collective learning.
12. Turn lessons into action items.
Use this during post-incident planning.
Meaning: It makes improvement measurable.
Security Incident Response Steps For Beginners
1. Do not panic when an alert appears.
Use this when introducing incident response to someone new.
Meaning: It encourages calm decision-making.
2. Verify before acting.
Use this when a suspicious alert needs confirmation.
Meaning: It prevents unnecessary actions.
3. Follow the response plan.
Use this when established procedures are available.
Meaning: It keeps the response organized.
4. Ask for help when needed.
Use this when an incident exceeds your experience.
Meaning: It encourages appropriate escalation.
5. Record what you observe.
Use this when beginning an investigation.
Meaning: It preserves useful details.
6. Protect evidence.
Use this when investigating suspicious activity.
Meaning: It keeps important information available.
7. Identify affected systems.
Use this when trying to understand incident scope.
Meaning: It helps determine what may be involved.
8. Contain the problem carefully.
Use this when discussing the next response stage.
Meaning: It emphasizes limiting damage.
9. Remove the underlying threat.
Use this during remediation.
Meaning: It focuses on resolving the actual issue.
10. Recover with trusted resources.
Use this when restoring affected systems.
Meaning: It supports safer recovery.
11. Monitor after recovery.
Use this when systems are operational again.
Meaning: It helps catch recurring problems.
12. Learn from what happened.
Use this after the incident has ended.
Meaning: It turns experience into better preparation.
Confident Security Incident Response Steps
1. We have identified the issue, and we are responding.
Use this when communicating confidently during an active incident.
Meaning: It shows control without making unsupported promises.
2. The response is underway.
Use this when stakeholders need a concise progress update.
Meaning: It communicates action clearly.
3. We are prioritizing containment.
Use this when limiting further exposure is the immediate goal.
Meaning: It shows that response priorities are established.
4. The investigation is evidence-driven.
Use this when explaining the approach to analysis.
Meaning: It emphasizes facts over speculation.
5. We are assessing the full scope.
Use this when investigation is still ongoing.
Meaning: It communicates that conclusions are not premature.
6. Critical systems are receiving priority attention.
Use this when explaining response priorities.
Meaning: It shows risk-based decision-making.
7. We are preserving relevant evidence.
Use this when investigation and remediation overlap.
Meaning: It demonstrates disciplined response.
8. Remediation will follow verified findings.
Use this when explaining why actions are being sequenced.
Meaning: It supports deliberate decision-making.
9. Recovery will be validated before closure.
Use this when discussing the final response stage.
Meaning: It emphasizes thoroughness.
10. We are monitoring for further activity.
Use this after initial containment or recovery.
Meaning: It communicates continued vigilance.
11. The incident is being handled through established procedures.
Use this when stakeholders need reassurance about process.
Meaning: It signals structured management.
12. We will document the lessons and improve accordingly.
Use this after resolution.
Meaning: It shows commitment to continuous improvement.
Calm And Casual Security Incident Response Steps
1. Let’s take this one step at a time.
Use this when the team feels overwhelmed.
Meaning: It encourages calm and organized action.
2. First, let’s confirm what we know.
Use this when details are still unclear.
Meaning: It separates facts from assumptions.
3. No need to rush into guesses.
Use this when speculation is spreading.
Meaning: It encourages evidence-based thinking.
4. We can work through this systematically.
Use this when reassuring a colleague.
Meaning: It reinforces an organized approach.
5. Let’s check the evidence before deciding.
Use this when multiple explanations are possible.
Meaning: It promotes careful analysis.
6. Contain first, solve the rest next.
Use this when prioritizing immediate risk reduction.
Meaning: It simplifies the response sequence.
7. We have a plan, so let’s use it.
Use this when established procedures exist.
Meaning: It encourages following the response process.
8. Keep the updates coming, but keep them clear.
Use this during team communication.
Meaning: It encourages useful information sharing.
9. Let’s document it while it is fresh.
Use this after an important discovery.
Meaning: It promotes timely documentation.
10. One problem at a time.
Use this when several issues appear together.
Meaning: It encourages manageable progress.
11. We will know more after the investigation.
Use this when people demand immediate answers.
Meaning: It acknowledges uncertainty honestly.
12. Once it is stable, we will review everything.
Use this after immediate response actions.
Meaning: It separates urgent work from later analysis.
Clever Security Incident Response Steps
1. Follow the evidence, not the drama.
Use this when an incident creates unnecessary speculation.
Meaning: It prioritizes facts over emotional reactions.
2. An alert is a clue, not a conclusion.
Use this when explaining why validation matters.
Meaning: It distinguishes detection from confirmation.
3. Containment buys us breathing room.
Use this when explaining the purpose of isolation.
Meaning: It shows how containment supports investigation.
4. The timeline tells the story.
Use this when reconstructing incident activity.
Meaning: It highlights the importance of chronology.
5. Scope before assumptions.
Use this when deciding how widely an incident may have spread.
Meaning: It encourages evidence-based scoping.
6. Fix the entry point, not just the symptoms.
Use this when discussing remediation.
Meaning: It emphasizes addressing underlying causes.
7. Recovery is not the same as closure.
Use this after systems are restored.
Meaning: It reminds teams that validation still matters.
8. Every incident leaves a lesson.
Use this during post-incident review.
Meaning: It emphasizes continuous improvement.
9. Logs can turn suspicion into evidence.
Use this when explaining log analysis.
Meaning: It highlights the value of recorded activity.
10. Good response is controlled response.
Use this when discussing incident management.
Meaning: It connects effectiveness with discipline.
11. Fast does not have to mean careless.
Use this when balancing speed and accuracy.
Meaning: It encourages efficient but thoughtful action.
12. The best incident response ends with stronger defenses.
Use this after an incident review.
Meaning: It connects response work with future resilience.
Emergency Security Incident Response Steps
1. Confirm the emergency.
Use this when a high-priority security event is reported.
Meaning: It ensures the response matches the actual severity.
2. Activate the appropriate response team.
Use this when additional expertise is required.
Meaning: It brings the right people into the response.
3. Protect critical systems immediately.
Use this when important services may be exposed.
Meaning: It prioritizes essential assets.
4. Establish clear communication.
Use this when multiple teams must coordinate quickly.
Meaning: It reduces confusion during urgent response.
5. Contain the highest-risk activity.
Use this when immediate exposure needs to be reduced.
Meaning: It focuses attention on the most urgent threat.
6. Preserve critical evidence.
Use this when urgent action could affect investigation material.
Meaning: It protects useful forensic information.
7. Identify the most affected assets.
Use this when the incident scope is still developing.
Meaning: It helps prioritize response.
8. Escalate according to severity.
Use this when leadership or specialist teams may need involvement.
Meaning: It supports appropriate decision-making.
9. Provide verified status updates.
Use this when stakeholders need information quickly.
Meaning: It prevents rumors from replacing facts.
10. Stabilize affected services.
Use this when operational disruption is occurring.
Meaning: It focuses on restoring control.
11. Validate recovery before normal operations.
Use this when systems are returning to service.
Meaning: It reduces the risk of repeating the incident.
12. Conduct a detailed review afterward.
Use this once the emergency has ended.
Meaning: It identifies improvements for future events.
Security Incident Response Steps For Reports
1. State what happened clearly.
Use this as the opening of an incident report.
Meaning: It gives readers a direct summary.
2. Record when the incident was detected.
Use this when establishing the response timeline.
Meaning: It identifies the initial detection point.
3. Describe affected systems.
Use this when documenting incident scope.
Meaning: It explains which assets were involved.
4. Summarize the investigation.
Use this when explaining analytical findings.
Meaning: It provides context for response decisions.
5. Document containment actions.
Use this after immediate risk reduction measures.
Meaning: It records how the incident was controlled.
6. Record eradication activities.
Use this when documenting threat removal.
Meaning: It explains how the underlying issue was addressed.
7. Describe recovery actions.
Use this when documenting restoration.
Meaning: It shows how normal operations returned.
8. Include verified impact information.
Use this when describing consequences.
Meaning: It keeps the report factual.
9. Identify outstanding risks.
Use this when some investigation remains open.
Meaning: It communicates unresolved concerns.
10. Record important decisions and approvals.
Use this when accountability matters.
Meaning: It creates a reliable decision trail.
11. Summarize lessons learned.
Use this after the response concludes.
Meaning: It captures improvement opportunities.
12. List recommended follow-up actions.
Use this at the end of an incident report.
Meaning: It turns findings into practical next steps.
FAQs
What The Phrase Means
Security incident response steps are the organized actions used to detect, investigate, contain, remove, and recover from security incidents.
Emotional Or Flirty Interpretations
The phrase is technical rather than emotional or flirty, so it normally has no romantic meaning.
Professional Or Formal Usage
In professional settings, the phrase describes a structured cybersecurity process for managing security incidents.
What To Say If You Don’t Actually Mean It
Say what you actually know, rather than pretending an incident response process has started.
Whether Humor Is Appropriate
Light humor can help teams stay calm, but serious incidents require clear and professional communication.
Conclusion
Knowing the right security incident response steps can turn a stressful security alert into a structured action plan. The biggest win is not sounding like a cybersecurity superhero. It is staying calm, checking the facts, communicating clearly, and following a process that limits damage.
Whether you are writing an incident report, explaining cybersecurity to coworkers, studying for a certification, or simply trying to understand how incident response works, the right words can make complicated situations easier to handle.
Try different response styles depending on your audience, save the ideas that fit your workflow, and share this guide with someone who might need it during their next security moment. Stay sharp, stay prepared, and keep improving your response game.