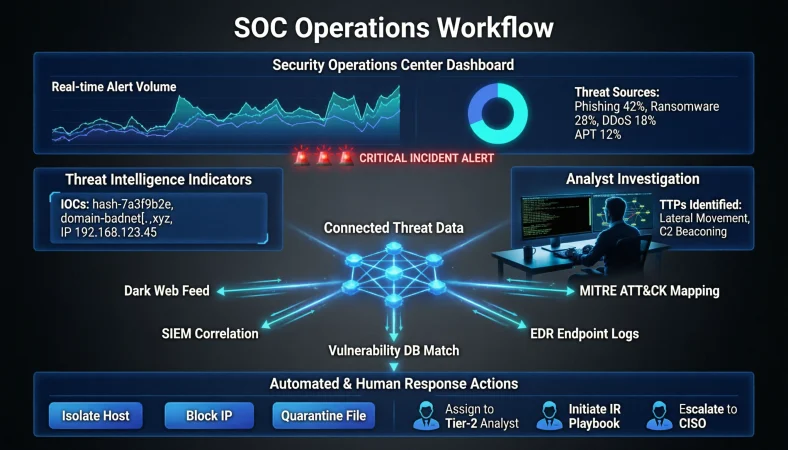
Quick Answer: Incident response with threat intelligence combines real-time security incident handling with intelligence about threats, attackers, indicators, tactics, and techniques. It helps security teams move from simply reacting to incidents to understanding what is happening and responding with better context.
Top alternatives: threat-informed incident response, intelligence-driven incident response, cyber threat intelligence response, incident response intelligence, threat intelligence integration
When a security alert suddenly lights up your dashboard, nobody wants to spend ten minutes wondering what it means. Whether you’re discussing cybersecurity in a workplace, explaining a SOC process to a colleague, answering a technical question, or posting about incident response online, incident response with threat intelligence is a phrase worth understanding. It connects two important ideas: responding quickly to suspicious activity and using threat intelligence to add context to that response. Instead of treating every alert like an isolated fire drill, analysts can use indicators, attacker behaviors, known campaigns, and relevant threat information to help prioritize and investigate incidents. The right explanation can make a complicated cybersecurity topic much easier to understand. And honestly, when your inbox already has 47 alerts, clarity is a beautiful thing.
Funny Incident Response With Threat Intelligence Responses
“It is basically incident response with receipts.”
Use this when casually explaining how threat intelligence adds context to an investigation.
Meaning: It humorously describes intelligence as supporting evidence for security decisions.
“The alert showed up, and threat intelligence brought the backstory.”
Use this when explaining why context matters during incident handling.
Meaning: It describes intelligence as additional information surrounding an alert.
“We are not just chasing alerts anymore.”
Use this when explaining a more intelligence-driven security workflow.
Meaning: It suggests analysts can prioritize incidents using additional context.
“The SOC got a mystery, and threat intelligence brought clues.”
Use this as a light cybersecurity presentation line.
Meaning: It compares incident investigation with solving a mystery.
“An indicator without context is just a very suspicious breadcrumb.”
Use this when explaining why raw indicators may need enrichment.
Meaning: It emphasizes the value of context around security indicators.
“The firewall saw something weird, so naturally we opened the detective agency.”
Use this as a humorous cybersecurity caption.
Meaning: It compares security investigation with detective work.
“Threat intelligence said, ‘Here is what this alert might actually mean.’”
Use this when describing contextual enrichment.
Meaning: It explains how intelligence can help analysts understand alerts.
“Cybersecurity: where the plot twist is usually an IP address.”
Use this as a playful social caption about investigations.
Meaning: It jokes about indicators appearing during security incidents.
“Incident response gets less chaotic when the clues arrive early.”
Use this when explaining the value of timely intelligence.
Meaning: It highlights how context can support faster decision-making.
“The alert was loud, but the intelligence made it useful.”
Use this when discussing alert enrichment.
Meaning: It distinguishes notification volume from actionable information.
“We brought threat intelligence to the incident party.”
Use this when introducing intelligence integration in a casual presentation.
Meaning: It describes adding threat context to incident response.
“Nothing says teamwork like analysts, alerts, and a mountain of context.”
Use this as a humorous SOC-related caption.
Meaning: It captures the collaborative nature of intelligence-driven response.
Professional Incident Response With Threat Intelligence Responses
“Threat intelligence provides context that can support incident prioritization and investigation.”
Use this in a workplace discussion or security report.
Meaning: It explains the practical role of intelligence during response.
“Incident response can benefit from intelligence about relevant threats, indicators, and adversary behavior.”
Use this when explaining the relationship between the two disciplines.
Meaning: It connects threat information with response activities.
“Threat intelligence can help analysts determine whether an indicator is relevant to an active incident.”
Use this during a technical presentation.
Meaning: It highlights contextual validation.
“An intelligence-driven response can improve the quality of investigation decisions.”
Use this in a cybersecurity strategy discussion.
Meaning: It emphasizes informed decision-making.
“Relevant threat context can help security teams prioritize incidents according to potential risk.”
Use this in a professional report.
Meaning: It explains how intelligence can support prioritization.
“Incident response and threat intelligence work best when information flows between both functions.”
Use this when discussing security operations.
Meaning: It emphasizes continuous information sharing.
“Threat intelligence should be relevant, timely, and actionable for incident responders.”
Use this when defining useful intelligence.
Meaning: It describes qualities that make intelligence valuable during response.
“Indicators should be evaluated within the broader context of the incident.”
Use this when reviewing investigation procedures.
Meaning: It discourages treating individual indicators as complete evidence.
“Threat intelligence can support detection, investigation, containment, and recovery activities.”
Use this in a cybersecurity planning document.
Meaning: It describes how intelligence can contribute throughout the response lifecycle.
“Incident responders can use intelligence to understand potential adversary activity.”
Use this when explaining analyst workflows.
Meaning: It connects threat knowledge with investigation.
“Effective integration requires communication between intelligence and response teams.”
Use this during a security operations meeting.
Meaning: It emphasizes collaboration between functions.
“The goal is not simply more intelligence, but intelligence that improves response decisions.”
Use this when discussing program effectiveness.
Meaning: It focuses attention on practical value rather than information volume.
Clever Incident Response With Threat Intelligence Responses
“An alert tells you what happened; intelligence can help explain the bigger picture.”
Use this when teaching the difference between detection and context.
Meaning: It separates immediate notification from broader threat understanding.
“Context turns an indicator into something investigators can evaluate.”
Use this when explaining threat intelligence enrichment.
Meaning: It highlights why context matters around indicators.
“The value of intelligence appears when it changes a response decision.”
Use this during a security strategy discussion.
Meaning: It defines useful intelligence by its operational impact.
“Threat intelligence connects isolated signals with broader threat patterns.”
Use this when explaining intelligence analysis.
Meaning: It describes how multiple pieces of information can become more meaningful together.
“Incident response asks what we should do next; intelligence helps inform that question.”
Use this when explaining the relationship between disciplines.
Meaning: It describes intelligence as decision-support information.
“A useful indicator needs more than a match; it needs context.”
Use this when discussing indicator enrichment.
Meaning: It warns against interpreting matches without additional information.
“Threat intelligence gives incident responders another lens.”
Use this when introducing intelligence integration.
Meaning: It describes intelligence as an additional perspective during investigations.
“Good response is fast; informed response is fast with context.”
Use this as a cybersecurity presentation line.
Meaning: It emphasizes combining speed with informed decisions.
“Threat intelligence can turn scattered observations into an investigation hypothesis.”
Use this when discussing analytical workflows.
Meaning: It explains how intelligence can help form investigative ideas.
“The strongest response process connects detection, context, action, and learning.”
Use this in a security operations discussion.
Meaning: It describes an integrated response cycle.
“Intelligence is useful when it answers a question the responder actually has.”
Use this when discussing operational relevance.
Meaning: It emphasizes that intelligence should solve practical problems.
“The incident is the event; intelligence helps explain the environment around it.”
Use this when giving a concise conceptual explanation.
Meaning: It distinguishes the incident from surrounding threat context.
Concise Incident Response With Threat Intelligence Responses
“Threat intelligence adds context to incident response.”
Use this as a short definition in a presentation.
Meaning: It summarizes the relationship in one sentence.
“It helps responders make more informed decisions.”
Use this when explaining the primary benefit.
Meaning: It highlights decision support.
“Intelligence can help prioritize relevant incidents.”
Use this when discussing alert triage.
Meaning: It connects threat information with prioritization.
“Indicators can be enriched with additional threat context.”
Use this when describing investigation workflows.
Meaning: It explains how raw indicators become more useful.
“Threat intelligence can support investigation and containment.”
Use this in a cybersecurity overview.
Meaning: It identifies practical response applications.
“Response teams can use intelligence to understand potential adversary behavior.”
Use this in a technical explanation.
Meaning: It connects intelligence with behavioral analysis.
“Relevant intelligence can reduce uncertainty during an incident.”
Use this when discussing investigation challenges.
Meaning: It describes one potential benefit of contextual information.
“Incident response provides action, while intelligence provides context.”
Use this when teaching the relationship.
Meaning: It offers a simple conceptual distinction.
“The two functions become stronger when they share information.”
Use this in a team discussion.
Meaning: It emphasizes collaboration.
“Threat intelligence can help connect alerts to known threat activity.”
Use this when explaining correlation.
Meaning: It describes how intelligence may add relevance to an alert.
“Good intelligence supports practical response decisions.”
Use this in a security strategy conversation.
Meaning: It focuses on operational usefulness.
“The goal is informed action, not information overload.”
Use this when discussing intelligence management.
Meaning: It emphasizes quality and relevance over volume.
Technical Incident Response With Threat Intelligence Responses
“Threat intelligence can enrich incident indicators with contextual information.”
Use this in a technical security discussion.
Meaning: It describes the enrichment process.
“Incident responders can correlate observed activity with relevant threat intelligence.”
Use this when explaining analytical workflows.
Meaning: It describes comparing incident evidence with known information.
“Threat intelligence can include indicators, tactics, techniques, procedures, and campaign context.”
Use this when explaining intelligence categories.
Meaning: It outlines common forms of threat information.
“Intelligence integration can support triage and investigation workflows.”
Use this in a security operations presentation.
Meaning: It describes practical integration points.
“Contextual enrichment can help analysts evaluate the significance of an indicator.”
Use this when discussing alert analysis.
Meaning: It explains how context supports interpretation.
“Threat intelligence feeds can provide external information that complements internal telemetry.”
Use this when discussing security data sources.
Meaning: It describes how external intelligence can supplement internal observations.
“Intelligence should be evaluated for relevance before being used operationally.”
Use this when discussing intelligence quality.
Meaning: It emphasizes that not every piece of intelligence is equally useful.
“Incident response teams can use threat information to develop investigation hypotheses.”
Use this during an analytical workflow discussion.
Meaning: It connects intelligence with investigative reasoning.
“Threat intelligence can help identify relationships between seemingly separate events.”
Use this when explaining correlation.
Meaning: It describes how broader context may reveal connections.
“The integration of intelligence and response should account for timeliness and confidence.”
Use this in a security architecture discussion.
Meaning: It highlights important characteristics of operational intelligence.
“Response actions should remain grounded in validated incident evidence.”
Use this when discussing responsible use of intelligence.
Meaning: It emphasizes verification before action.
“Threat intelligence should complement, rather than replace, internal investigation.”
Use this when explaining proper analytical balance.
Meaning: It warns against relying solely on external intelligence.
Friendly Incident Response With Threat Intelligence Responses
“Think of threat intelligence as extra context for the security team.”
Use this when explaining the topic to a beginner.
Meaning: It makes the concept approachable.
“It helps turn a confusing alert into a question we can investigate.”
Use this when explaining incident triage.
Meaning: It describes how context can guide investigation.
“The more useful context you have, the easier it can be to understand an alert.”
Use this in an introductory cybersecurity conversation.
Meaning: It highlights the role of relevant information.
“Incident response handles the problem while intelligence helps explain it.”
Use this when teaching the basic relationship.
Meaning: It gives a simple distinction between the functions.
“Threat intelligence can give responders a little more visibility.”
Use this when explaining intelligence enrichment casually.
Meaning: It describes additional context without overcomplicating it.
“It is about knowing what you are looking at before making a decision.”
Use this when explaining informed response.
Meaning: It emphasizes context before action.
“A suspicious signal becomes easier to investigate when you know its background.”
Use this when discussing indicator context.
Meaning: It explains why background information matters.
“Good intelligence helps answer the ‘so what?’ behind an alert.”
Use this in a beginner-friendly presentation.
Meaning: It focuses on understanding significance.
“It is less about collecting everything and more about finding what matters.”
Use this when explaining intelligence quality.
Meaning: It emphasizes relevance.
“The security team gets clues, context, and a better starting point.”
Use this when summarizing the benefit of intelligence.
Meaning: It describes how intelligence can support investigation.
“Threat intelligence makes security conversations a little less mysterious.”
Use this as a friendly educational caption.
Meaning: It suggests that context improves understanding.
“When the alert gets complicated, context becomes your friend.”
Use this when explaining why enrichment matters.
Meaning: It presents context as useful support during investigations.
Sarcastic Incident Response With Threat Intelligence Responses
“Because apparently, one alert was not enough information.”
Use this when joking about enrichment and investigation.
Meaning: It humorously describes the need for additional context.
“Nothing like a mysterious indicator to improve everyone’s morning.”
Use this as a SOC humor caption.
Meaning: It jokes about unexpected security alerts.
“The alert says suspicious, so naturally we investigate everything.”
Use this when highlighting the importance of prioritization.
Meaning: It humorously points out why context is useful.
“Threat intelligence has entered the chat.”
Use this when introducing external context into an investigation.
Meaning: It playfully describes intelligence joining the response process.
“Because guessing is obviously a security strategy.”
Use this sarcastically when emphasizing informed decisions.
Meaning: It argues humorously for evidence and context.
“The indicator looked harmless until the context arrived.”
Use this when discussing enrichment.
Meaning: It illustrates how additional information can change interpretation.
“Another day, another suspicious artifact asking for attention.”
Use this as a relatable SOC caption.
Meaning: It jokes about the constant flow of security alerts.
“The incident was simple until someone asked for the full context.”
Use this when joking about investigations.
Meaning: It highlights how deeper analysis can reveal complexity.
“Nothing says productivity like investigating an IP address at midnight.”
Use this as a cybersecurity meme-style caption.
Meaning: It humorously depicts after-hours incident investigation.
“The dashboard said ‘urgent,’ so we asked for evidence.”
Use this when promoting careful triage.
Meaning: It emphasizes validating alerts before acting.
“Threat intelligence: because security teams apparently enjoy more tabs.”
Use this when joking about analysts using multiple information sources.
Meaning: It humorously references the information-heavy nature of investigations.
“We have alerts, indicators, context, and approximately zero free browser tabs.”
Use this as a social media caption for security professionals.
Meaning: It jokes about the workload involved in threat investigation.
Creative Incident Response With Threat Intelligence Responses
“Think of incident response as the action and threat intelligence as the map.”
Use this when creating an easy analogy for beginners.
Meaning: It describes intelligence as guidance for response activity.
“Threat intelligence gives the incident a backstory.”
Use this when explaining contextual information.
Meaning: It describes how intelligence can explain surrounding threat activity.
“Every alert is a clue, but not every clue deserves the same attention.”
Use this when discussing prioritization.
Meaning: It explains why contextual assessment matters.
“Threat intelligence helps connect the dots between isolated signals.”
Use this in an educational cybersecurity post.
Meaning: It describes correlation across events.
“Incident response is where information turns into action.”
Use this when explaining the purpose of response teams.
Meaning: It describes the operational nature of incident response.
“Threat intelligence helps put the puzzle pieces in context.”
Use this when explaining enrichment to beginners.
Meaning: It presents intelligence as contextual support.
“The alert is the headline; intelligence helps fill in the article.”
Use this as a memorable analogy.
Meaning: It distinguishes an initial notification from deeper context.
“A security incident is easier to understand when the clues have a timeline.”
Use this when discussing investigation context.
Meaning: It emphasizes chronology during incident analysis.
“Threat intelligence turns isolated signals into a bigger security story.”
Use this as an educational caption.
Meaning: It describes the value of connecting related information.
“The best response stories start with useful evidence.”
Use this when discussing investigation quality.
Meaning: It emphasizes evidence-based response.
“Intelligence is the context between detection and decision.”
Use this when presenting a conceptual model.
Meaning: It explains where intelligence can fit within response workflows.
“When the security picture gets blurry, context helps sharpen the view.”
Use this as a creative explanation.
Meaning: It describes how relevant intelligence can reduce uncertainty.
Chill And Casual Incident Response With Threat Intelligence Responses
“Basically, threat intelligence helps us understand what an alert might mean.”
Use this when explaining the topic casually.
Meaning: It gives a simple description of intelligence enrichment.
“It is like adding context to a security alert.”
Use this when someone asks for the simplest explanation.
Meaning: It compares intelligence with contextual information.
“We look at the alert, then check what else we know about it.”
Use this when describing an investigation casually.
Meaning: It summarizes contextual analysis.
“The goal is to respond with more information and less guessing.”
Use this when explaining intelligence-driven response.
Meaning: It emphasizes informed decisions.
“Threat intelligence helps us see beyond the individual alert.”
Use this when discussing broader context.
Meaning: It describes looking at surrounding threat information.
“It can help tell us whether something deserves more attention.”
Use this when explaining prioritization.
Meaning: It connects intelligence with triage.
“Incident response is the action; intelligence is part of the context.”
Use this when introducing the concept.
Meaning: It gives a simple distinction.
“The useful part is knowing what the signal connects to.”
Use this when discussing indicator relationships.
Meaning: It emphasizes contextual connections.
“You do not want more alerts; you want more useful information.”
Use this when discussing security operations.
Meaning: It focuses on actionable context.
“It is basically security investigation with better background information.”
Use this for a casual explanation.
Meaning: It describes intelligence-supported investigation.
“Good context can make a confusing incident easier to follow.”
Use this when discussing investigation workflows.
Meaning: It describes the practical value of context.
“The simple version: detect, understand, respond, learn.”
Use this when summarizing an intelligence-informed response cycle.
Meaning: It presents a concise conceptual workflow.
Confident Incident Response With Threat Intelligence Responses
“Threat intelligence strengthens incident response by adding relevant context.”
Use this in a confident security presentation.
Meaning: It clearly states the relationship between the functions.
“An informed response starts with understanding the incident.”
Use this when explaining response strategy.
Meaning: It emphasizes investigation before action.
“Relevant intelligence can help responders prioritize what deserves attention.”
Use this during a security operations discussion.
Meaning: It connects intelligence with triage.
“Incident response becomes more informed when internal evidence meets external context.”
Use this in a cybersecurity presentation.
Meaning: It describes combining organizational telemetry with threat information.
“Threat intelligence can help responders investigate potential adversary behavior.”
Use this when describing analyst responsibilities.
Meaning: It connects intelligence with behavioral investigation.
“Context supports better questions, and better questions support better investigations.”
Use this as a security awareness statement.
Meaning: It explains how context can improve analytical reasoning.
“The objective is actionable intelligence that supports real response decisions.”
Use this when discussing program goals.
Meaning: It focuses on operational usefulness.
“Response teams should know why an indicator matters, not just that it matched.”
Use this when explaining contextual analysis.
Meaning: It emphasizes understanding significance.
“Threat intelligence should be integrated where it can influence investigation or response.”
Use this during security architecture planning.
Meaning: It focuses on practical integration.
“Strong response processes connect detection, investigation, intelligence, and action.”
Use this when describing an integrated SOC workflow.
Meaning: It presents the disciplines as connected functions.
“Intelligence is most valuable when responders can act on it.”
Use this when discussing operationalization.
Meaning: It emphasizes practical usability.
“The right context can transform an uncertain alert into a focused investigation.”
Use this when explaining intelligence enrichment.
Meaning: It describes how context can improve investigative direction.
Analytical Incident Response With Threat Intelligence Responses
“Threat intelligence helps analysts place incident evidence into a broader threat context.”
Use this in an analytical report.
Meaning: It explains the contextual role of intelligence.
“Correlation can reveal relationships that are difficult to see from a single event.”
Use this when discussing security analytics.
Meaning: It explains why combining information can be useful.
“Confidence, relevance, and timeliness are important when evaluating threat intelligence.”
Use this in an intelligence program discussion.
Meaning: It identifies key considerations for useful intelligence.
“An indicator should be evaluated according to the incident context in which it appears.”
Use this when discussing investigation methodology.
Meaning: It discourages isolated interpretation.
“Threat intelligence can support hypothesis development during incident investigation.”
Use this in an analyst training session.
Meaning: It describes how intelligence can guide questions for investigation.
“Incident response benefits when intelligence is translated into operational decisions.”
Use this when discussing intelligence operationalization.
Meaning: It emphasizes moving from information to action.
“Historical threat information can provide useful context when investigating current activity.”
Use this when explaining intelligence sources.
Meaning: It describes how past information can inform analysis without replacing current evidence.
“Behavioral context can complement indicator-based investigation.”
Use this when discussing adversary tactics and techniques.
Meaning: It explains the value of looking beyond individual indicators.
“The quality of an intelligence-driven response depends on the quality of the information supporting it.”
Use this in a security strategy discussion.
Meaning: It emphasizes information quality.
“Threat intelligence can help analysts distinguish relevant signals from background noise.”
Use this when discussing alert triage.
Meaning: It describes prioritization through contextual information.
“A mature workflow continuously feeds investigation findings back into intelligence processes.”
Use this when discussing organizational learning.
Meaning: It describes a feedback loop between response and intelligence.
“The strongest analysis combines technical evidence with relevant contextual information.”
Use this when summarizing investigative principles.
Meaning: It emphasizes a balanced analytical approach.
Strategic Incident Response With Threat Intelligence Responses
“Threat intelligence should support the organization’s incident response objectives.”
Use this when discussing cybersecurity strategy.
Meaning: It connects intelligence activities with response goals.
“The integration should focus on information that can influence security decisions.”
Use this during program planning.
Meaning: It emphasizes operational relevance.
“Intelligence requirements should reflect the questions incident responders actually need answered.”
Use this when designing an intelligence program.
Meaning: It encourages responder-driven intelligence needs.
“Incident findings can help refine future intelligence requirements.”
Use this when discussing continuous improvement.
Meaning: It describes how response experiences can improve intelligence collection.
“A feedback loop between response and intelligence can strengthen organizational learning.”
Use this in a cybersecurity strategy presentation.
Meaning: It describes continuous information sharing.
“Threat intelligence should be integrated into workflows rather than treated as a separate information stream.”
Use this when discussing operational maturity.
Meaning: It emphasizes practical integration.
“The value of intelligence should be measured by how effectively it supports decisions.”
Use this when discussing program evaluation.
Meaning: It focuses on outcomes rather than information volume.
“Response teams need timely intelligence when incidents are unfolding.”
Use this when discussing operational requirements.
Meaning: It emphasizes the importance of timely information.
“Strategic intelligence can help connect individual incidents to broader organizational risks.”
Use this when discussing security planning.
Meaning: It connects incident-level information with larger risk considerations.
“Incident response provides lessons that can improve future defensive priorities.”
Use this when discussing post-incident learning.
Meaning: It describes how response outcomes can inform future security work.
“Threat intelligence becomes more useful when it is aligned with business and security priorities.”
Use this in a security leadership discussion.
Meaning: It emphasizes alignment with organizational objectives.
“The goal is a repeatable process where intelligence informs response and response improves intelligence.”
Use this when summarizing an integrated strategy.
Meaning: It describes a continuous improvement cycle.
Educational Incident Response With Threat Intelligence Responses
“Incident response is about handling a security event, while threat intelligence adds information about the threat landscape.”
Use this when teaching the basics.
Meaning: It distinguishes the two disciplines while showing their relationship.
“Threat intelligence can help explain why an indicator may matter.”
Use this when teaching indicator analysis.
Meaning: It emphasizes context.
“A security alert is a starting point, not always the final answer.”
Use this when teaching incident triage.
Meaning: It encourages investigation.
“Threat intelligence can provide clues about tactics, techniques, and known activity.”
Use this in an introductory cybersecurity lesson.
Meaning: It explains common intelligence content.
“Incident responders use evidence to understand what happened and decide what to do next.”
Use this when explaining the response process.
Meaning: It summarizes the role of responders.
“Intelligence can help connect technical observations with broader threat information.”
Use this when explaining correlation.
Meaning: It describes contextual analysis.
“Good intelligence answers useful questions instead of simply adding more data.”
Use this when teaching intelligence quality.
Meaning: It emphasizes relevance.
“Threat intelligence and incident response work together through information sharing.”
Use this when teaching security operations.
Meaning: It highlights collaboration.
“The response process can create new information that improves future intelligence.”
Use this when discussing feedback loops.
Meaning: It explains organizational learning.
“An indicator becomes more useful when analysts understand its context.”
Use this when teaching enrichment.
Meaning: It explains why context matters.
“Incident response turns observations into actions.”
Use this when teaching response fundamentals.
Meaning: It summarizes the operational role of response.
“Threat intelligence helps responders make sense of the bigger picture.”
Use this as a simple closing statement for a lesson.
Meaning: It describes intelligence as broader context.
Strategic And Executive Incident Response With Threat Intelligence Responses
“Threat intelligence can help provide decision-makers with relevant context during significant incidents.”
Use this in an executive cybersecurity briefing.
Meaning: It describes intelligence as decision-support information.
“Incident response should provide clear information about impact, evidence, and response actions.”
Use this when preparing leadership updates.
Meaning: It emphasizes concise incident communication.
“Threat context can help explain why an incident deserves particular attention.”
Use this during a management discussion.
Meaning: It connects intelligence with prioritization.
“Security leadership benefits from timely information that supports risk-based decisions.”
Use this when discussing executive reporting.
Meaning: It focuses on useful information for decision-makers.
“Intelligence can help connect technical findings with broader security concerns.”
Use this when translating technical issues for leadership.
Meaning: It explains how context bridges technical and strategic discussions.
“Incident response and threat intelligence should support a common understanding of security risk.”
Use this in a leadership presentation.
Meaning: It emphasizes alignment.
“Relevant threat information can help teams communicate incident significance more clearly.”
Use this when preparing an incident briefing.
Meaning: It describes the communication value of context.
“The goal is to provide leaders with information they can use to make informed decisions.”
Use this when explaining executive security reporting.
Meaning: It focuses on actionable communication.
“A mature response process turns incident lessons into future security improvements.”
Use this when discussing post-incident strategy.
Meaning: It highlights continuous improvement.
“Threat intelligence can help organizations understand whether observed activity aligns with known threat patterns.”
Use this in an executive-level technical discussion.
Meaning: It describes one way intelligence can add context.
“Clear communication matters as much as technical investigation during major incidents.”
Use this when discussing incident management.
Meaning: It emphasizes the importance of communicating findings effectively.
“The best security briefing is clear about what is known, what is uncertain, and what happens next.”
Use this when preparing an incident update.
Meaning: It encourages transparent and useful communication.
FAQs
What Does Incident Response With Threat Intelligence Mean?
Incident response with threat intelligence means using relevant threat information to add context to the detection, investigation, containment, and recovery of security incidents.
Why Is Threat Intelligence Useful During Incident Response?
It can help analysts understand indicators, prioritize activity, investigate potential adversary behavior, and make better-informed response decisions.
Is Incident Response The Same As Threat Intelligence?
No. Incident response focuses on handling security incidents, while threat intelligence focuses on collecting, analyzing, and communicating information about threats. They can work together closely.
What Is An Example Of Threat Intelligence In Incident Response?
An analyst might investigate a suspicious indicator and use relevant intelligence to determine whether it has been associated with known malicious activity or a particular threat pattern.
Is Incident Response With Threat Intelligence Used Professionally?
Yes. Security operations teams can integrate threat intelligence into alert triage, investigation, detection, incident handling, and post-incident analysis.
Can Threat Intelligence Help Prioritize Alerts?
It can provide contextual information that helps analysts assess relevance and potential significance, which may support prioritization.
What Should I Say If I Do Not Understand The Phrase?
A simple explanation is: “It means using threat information to better understand and respond to a security incident.”
Is Humor Appropriate When Discussing Incident Response?
Humor can work well in casual conversations, social posts, team culture, or educational content. Formal incident reports and executive communications usually benefit from clear and professional language.
Can Threat Intelligence Replace Incident Investigation?
No. Threat intelligence should complement internal evidence and investigation rather than replace validation of what is happening in the affected environment.
What Makes Threat Intelligence Useful To Responders?
Useful intelligence is generally relevant to the situation, timely enough to support decisions, understandable, and actionable.
How Do Incident Response And Threat Intelligence Work Together?
Threat intelligence can provide context during investigations, while incident response findings can generate information that improves future intelligence and defensive priorities.
What Is A Simple One-Line Explanation?
“Incident response handles the security event, while threat intelligence helps responders understand the threat context around it.”
Conclusion
Incident response with threat intelligence becomes much easier to understand when you think of it as action plus context. Incident responders investigate and handle security events, while relevant intelligence can help explain indicators, behaviors, relationships, and potential significance. The best response depends on the situation, so your wording should match your audience, whether you are chatting with a colleague, answering a technical question, writing a report, or creating cybersecurity content. Try the concise version for quick explanations, the professional responses for work, and the creative lines when you want your content to stand out. Save this guide, share it with your security-minded friends, and keep these responses ready for your next cybersecurity conversation.